Skip to content

European CTEM platform

blacklens.io: your attack surface under control

snapSEC GmbH's own platform shows your company through an attacker's eyes and tells you what to fix first.

Site plan of the attack surface of an example company: publicly reachable systems, cloud, internal network, a lookalike domain and dark web findings, with findings by severity. Illustration with sample data

Attack surface site plan

Illustration with sample data

AssetAreaFindingSeverity
remote.beispiel-gmbh.atbeispiel-gmbh.atRemote Desktop (RDP) reachable directly from the internetCritical
beisp1el-gmbh.atInternetLookalike domain, newly registeredHigh
Dark web sourcesInternetThree leaked credentials with addresses on the beispiel-gmbh.at domainHigh
test.beispiel-gmbh.atInternetNewly discovered test system, publicly reachableMedium
mail.beispiel-gmbh.atbeispiel-gmbh.atTLS certificate expires soonMedium
File serverInternal · SentryKnown vulnerability, update availableMedium
www.beispiel-gmbh.atbeispiel-gmbh.atNo open findingNo finding
Microsoft 365CloudNo open findingNo finding
AzureCloudNo open findingNo finding
OT networkInternal · SentryNo open findingNo finding
  • Developed and hosted in Europe
  • Scans only from AT, DE and CH
  • AI without external providers

Vorchdorf, Upper Austria ·47°59′ N · 13°55′ E

Overview

What is blacklens.io?

Continuous, not point-in-time: blacklens.io sees what changes on your attack surface and shows which finding to fix first.

blacklens.io is the attack surface management and continuous threat exposure management (CTEM) platform of snapSEC GmbH from Vorchdorf, Upper Austria. It continuously monitors external, internal and cloud assets, vulnerabilities and the dark web, and prioritises findings by real risk. Developed and hosted in Europe, it serves companies in Austria, Germany and Switzerland.

At a glance

blacklens.io
Vendor and operator
snapSEC GmbH, Vorchdorf (Upper Austria, Austria)
Category
Attack surface management and continuous threat exposure management (CTEM) as a SaaS platform
Modules
Attack surface, vulnerabilities (external, internal, cloud), dark web, Threat Center, supply chain, lookalike domains, PTaaS
Hosting
Developed and hosted in Europe, in ISO 27001 and SOC 2 certified data centres in the DACH region
Scan infrastructure
Exclusively in Austria, Germany and Switzerland
AI features
Self-hosted LLM, no external AI providers
Licence
By assets, every module in one licence, no public list prices
Try it
14 days free of charge, plus a free exposure check for your domain beforehand
Who it is for
Companies of all sizes in Austria, Germany and Switzerland

Capabilities

What does blacklens.io monitor?

blacklens.io continuously monitors your external, internal and cloud infrastructure, spots vulnerabilities before they are exploited and keeps an eye on the dark web as well.

Attack surface monitoring

Your attack surface as an attacker sees it

blacklens.io continuously finds everything that can be reached from the internet, including systems nobody keeps track of any more, and rates every asset by its risk.

  • Continuous discovery of publicly reachable assets and services
  • Uncover shadow IT, orphaned systems and misconfigurations
  • Detect lookalike domains that impersonate your brand
  • Ongoing monitoring with dynamic risk rating and an exposure score
Since the last scanblacklens.io

beispiel-gmbh.at3 changes

  • New serviceCriticalremote.beispiel-gmbh.atRemote Desktop (RDP) reachable directly from the internet
  • New domainHighbeisp1el-gmbh.atLookalike domain impersonating your brand
  • New hostMediumtest.beispiel-gmbh.atTest system outside the known perimeter

Illustration with sample data

Vulnerability management

Vulnerabilities prioritised by real risk

Not every vulnerability is equally urgent. blacklens.io shows what can actually be exploited and follows every finding until the fix is confirmed.

  • Automated vulnerability detection for internal, external and cloud infrastructure
  • Prioritisation by real exploitability and business risk
  • Technical hardening recommendations, explained by AI if you wish
  • Regular revalidation: fixed findings are re-checked and closed
  • Tickets and alerts in Jira, ServiceNow, Microsoft Teams, Slack or Microsoft Sentinel
What to fix firstblacklens.io

By CVSS alone

By real risk

  1. DatabaseCVSS 9.8
  2. VPN gatewayCVSS 8.1
  3. IntranetCVSS 7.5
  4. File serverCVSS 6.5
  5. PrinterCVSS 5.3
  1. 1VPN gatewayIn CISA KEV, public exploit
  2. 2File serverHigh EPSS, public exploit
  3. 3DatabaseNo known exploit, low EPSS
  4. 4IntranetLow EPSS
  5. 5PrinterNo known exploit

Illustration with sample data

Dark web monitoring & threat intelligence

Find leaked access before it is used

Stolen credentials are often traded before anyone notices an incident. blacklens.io reports matches for your domains so you can lock accounts and check devices.

  • Early detection of leaked credentials, infected devices and internal information
  • Monitoring of relevant marketplaces, forums and paste sites
  • Ransomware leak sites in view, including for your suppliers
  • Threat Center: new CVEs are matched against your technology inventory
  • Continuous threat analysis with active alerting
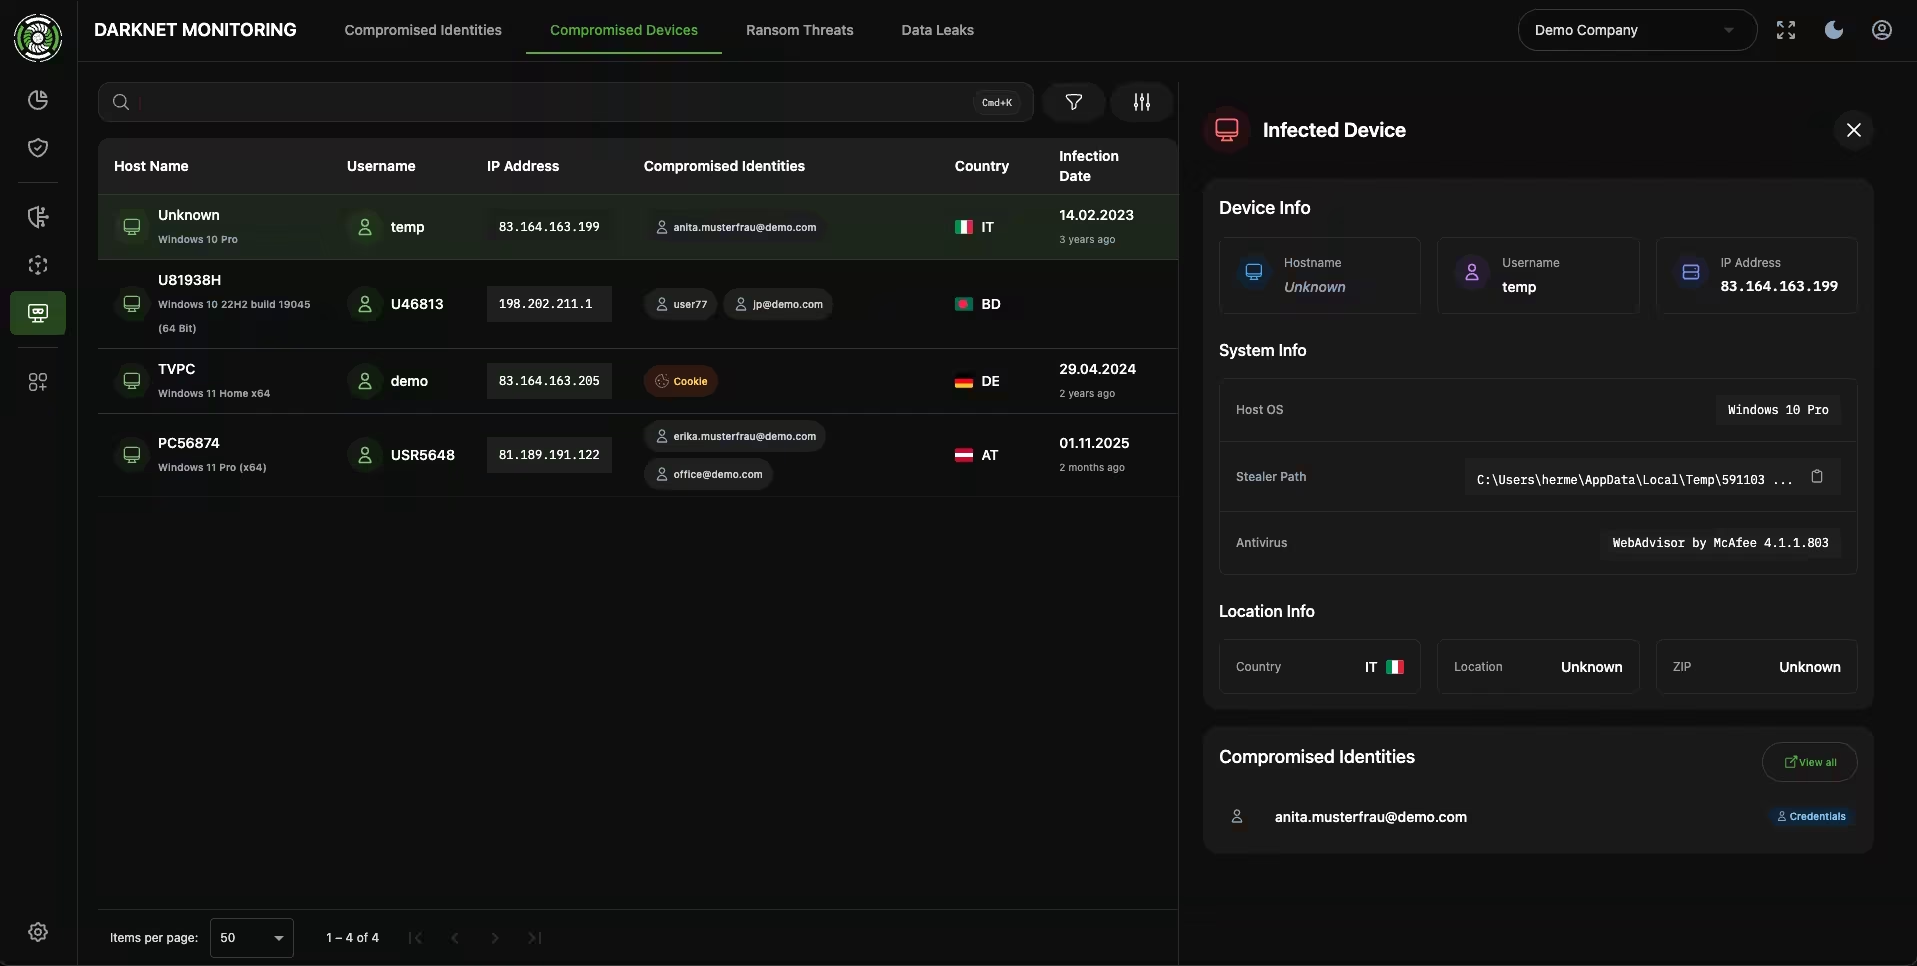
Dark web monitoringblacklens.io
Dark web monitoring in blacklens.io with demo data: list of compromised devices with host name, user name, IP address, affected identities, country and infection date.

Illustration with sample data

Platform

One platform, from source to fix

Every source feeds one analysis that prioritises by real risk. The result is tasks, reports and alerts where your team already works.

Sources

What attackers can see

  • ExternalDomains, IP addresses, services and technologies on the internet
  • Internal (Sentry)Scanner as a VM or Docker container for servers, clients, OT and Active Directory
  • CloudConnectors for Microsoft 365, Azure, AWS, Google Cloud, Cloudflare and Hetzner Cloud
  • Dark webLeaked credentials, infected devices and data leaks
  • Supply chainRansomware leak sites, matched against your supplier list

Analysis

Prioritised and easy to follow

  • Risk-based prioritisationEPSS, CISA KEV and exploit status instead of CVSS alone
  • Threat CenterEarly warning: new CVEs matched against your inventory in real time
  • AI explanationCause, impact and fix for every finding, explained by a self-hosted language model
  • Penetration testing as a servicePentesters confirm findings in the platform, with retests

Consistent severity levels across all sources

  • Critical
  • High
  • Medium
  • Low
  • Info

Action

Where your team works

  • One workflowAssign, fix and close automatically after the re-scan
  • ReportsExecutive, vulnerability and pentest reports, sent automatically on a schedule
  • IntegrationsJira, ServiceNow, Microsoft Teams, Slack and Microsoft Sentinel
  • REST APIFor your own portals, dashboards and automations

blacklens.io in numbers

assets monitored
1M+assets monitored
vulnerability tests, updated daily
200,000+vulnerability tests, updated daily
dark web leaks captured
50,000+dark web leaks captured

Figures from blacklens.io

How it fits

blacklens.io, penetration test or ACDC?

snapSEC's three business units answer different questions and work together: blacklens.io shows continuously what can be attacked, a penetration test checks how far an attacker gets, and ACDC detects attacks around the clock.

blacklens.io, penetration test or ACDC?
Aspectblacklens.ioPlatformPenetration testingConsultingACDC – Active Cyber Defense CenterManaged SOC
Key questionWhat can be attacked from outside, inside and in the cloud?How far does an attacker really get?Is someone attacking us right now?
CadenceContinuous and automatedPoint in time, individually scopedAround the clock (24/7)
Carried out byThe platform finds, your team fixessnapSEC pentesters, manually with tools and scriptsThe ACDC SOC team
OutcomePrioritised findings, alerts and reportsResults and hardening measures in a workshopDetected incidents, triage and agreed escalation

Why blacklens.io with snapSEC?

blacklens.io goes far beyond a traditional vulnerability scanner: the platform combines several security disciplines into a realistic picture of your threat landscape, continuous, automated and traceable at any time. For companies that think about security as a whole.

The vendor within reach
Development, operations and your named contact sit with one company: snapSEC GmbH from Vorchdorf, Upper Austria.
Have findings confirmed
Penetration testing as a service with retests right in the platform, or a tailored penetration test by snapSEC.
Connected to your operations
Alerts go to your ticketing system, chat or SIEM. For detection and response around the clock, there is ACDC.

Process

How to get started with blacklens.io

From a first look at your domain to continuous monitoring: you decide how deep you go.

  1. Free

    Exposure check

    Find out on blacklens.io what is publicly visible about your domain, before you commit to anything.

  2. Optional

    Demo or call

    We show you the platform for your use case and clarify scope and open questions.

  3. 14 days free

    Trial with your domain

    Try blacklens.io with your own domain and see real results for your attack surface instead of sample data.

  4. By assets

    Licence by scope

    Every module is included in one licence. The quote depends on the number of your assets.

FAQ

Questions about blacklens.io

What is attack surface management?

Attack surface management (ASM) is the continuous discovery, assessment and reduction of every point through which an attacker can reach a company: external, internal and in the cloud. Unlike a one-off scan, ASM runs all the time and reports changes such as new hosts, new services or new vulnerabilities. blacklens.io adds dark web signals and lookalike domains to this view, turning the inventory into a prioritised to-do list.

How does blacklens.io differ from a penetration test?

blacklens.io monitors your attack surface continuously and automatically, while a penetration test checks manually, at one point in time, how far an attacker really gets. The platform finds known vulnerabilities, misconfigurations and leaked credentials between two tests; pentesters find logic flaws and chained attacks that no scanner detects. The two complement each other: with penetration testing as a service, manual findings and retests land directly in blacklens.io, and snapSEC Consulting offers tailored penetration tests.

Where is the data processed?

blacklens.io is developed and hosted in Europe: the platform runs in data centres in the DACH region that are certified to ISO 27001 and SOC 2. The certificates apply to the data centres, not to snapSEC GmbH itself. Scans come exclusively from Austria, Germany and Switzerland. AI features run on a self-hosted large language model (LLM); no external AI providers are used.

How is blacklens.io licensed?

blacklens.io is licensed by scope, meaning the number of monitored assets, and every module is included in one licence. There are no public list prices because the price depends on your scope. You receive a quote after a short conversation with us or via blacklens.io. Before you decide, you can try the platform free of charge for 14 days with your own domain.

Can I try blacklens.io?

Yes, you can try blacklens.io free of charge for 14 days. For a first impression, the free exposure check on blacklens.io shows what is publicly visible about your domain. If you would rather see the platform first, book a demo or write to us via the contact form. We will then discuss your scope and the sensible next steps.

How are blacklens.io and snapSEC related?

blacklens.io is a platform of snapSEC GmbH: the Austrian cybersecurity company from Vorchdorf develops and operates it itself. blacklens.io is one of snapSEC's three business units, alongside ACDC (managed SOC) and consulting. You will find product details, the trial and the exposure check on www.blacklens.io. Conversations about deployment, licensing and combining it with penetration tests or ACDC take place directly with snapSEC.

Does blacklens.io help with NIS2?

Yes, blacklens.io supports technical measures that NIS2 requires, but it does not replace a legal assessment. Article 21 of Directive (EU) 2022/2555 calls for, among other things, vulnerability handling, supply chain security and asset management; in Austria, the NISG 2026 has been in force since 1 October 2026. blacklens.io provides the inventory, prioritised vulnerabilities, supplier monitoring and reports that document your vulnerability handling on an ongoing basis. Technical guidance, not legal advice.

Does blacklens.io also cover internal systems and the cloud?

Yes, besides the external attack surface, blacklens.io also checks internal networks and cloud accounts. Internally, the Sentry scanner runs as a virtual machine or Docker container in your network and checks servers, clients, OT devices and Active Directory. You connect cloud accounts such as Microsoft 365, Azure or AWS via connectors. All findings end up in the same inventory and the same workflow, with consistent severity levels.
blacklens.io with snapSEC

Make your attack surface visible now.

Talk to us: we will show you how blacklens.io complements your security strategy and reduces vulnerabilities over the long term.

Destination: snapSEC, Vorchdorf

snapSEC GmbH
Asamerstraße 1b
4655 Vorchdorf, Austria 47°59′ N · 13°55′ E

Personal, without obligation and confidential.